Secure by
architecture.
Security isn't a feature we bolted on — it's how the platform is built. Every layer is designed to protect your code, your data, and your customers.
Every app runs in its own isolated container with network policies that prevent cross-app access. Security scanning runs in the CI/CD pipeline on every release. Secrets are encrypted at rest and never touch logs or diffs. Authentication, permissions, and SSO are built into the platform — not add-ons you configure yourself.
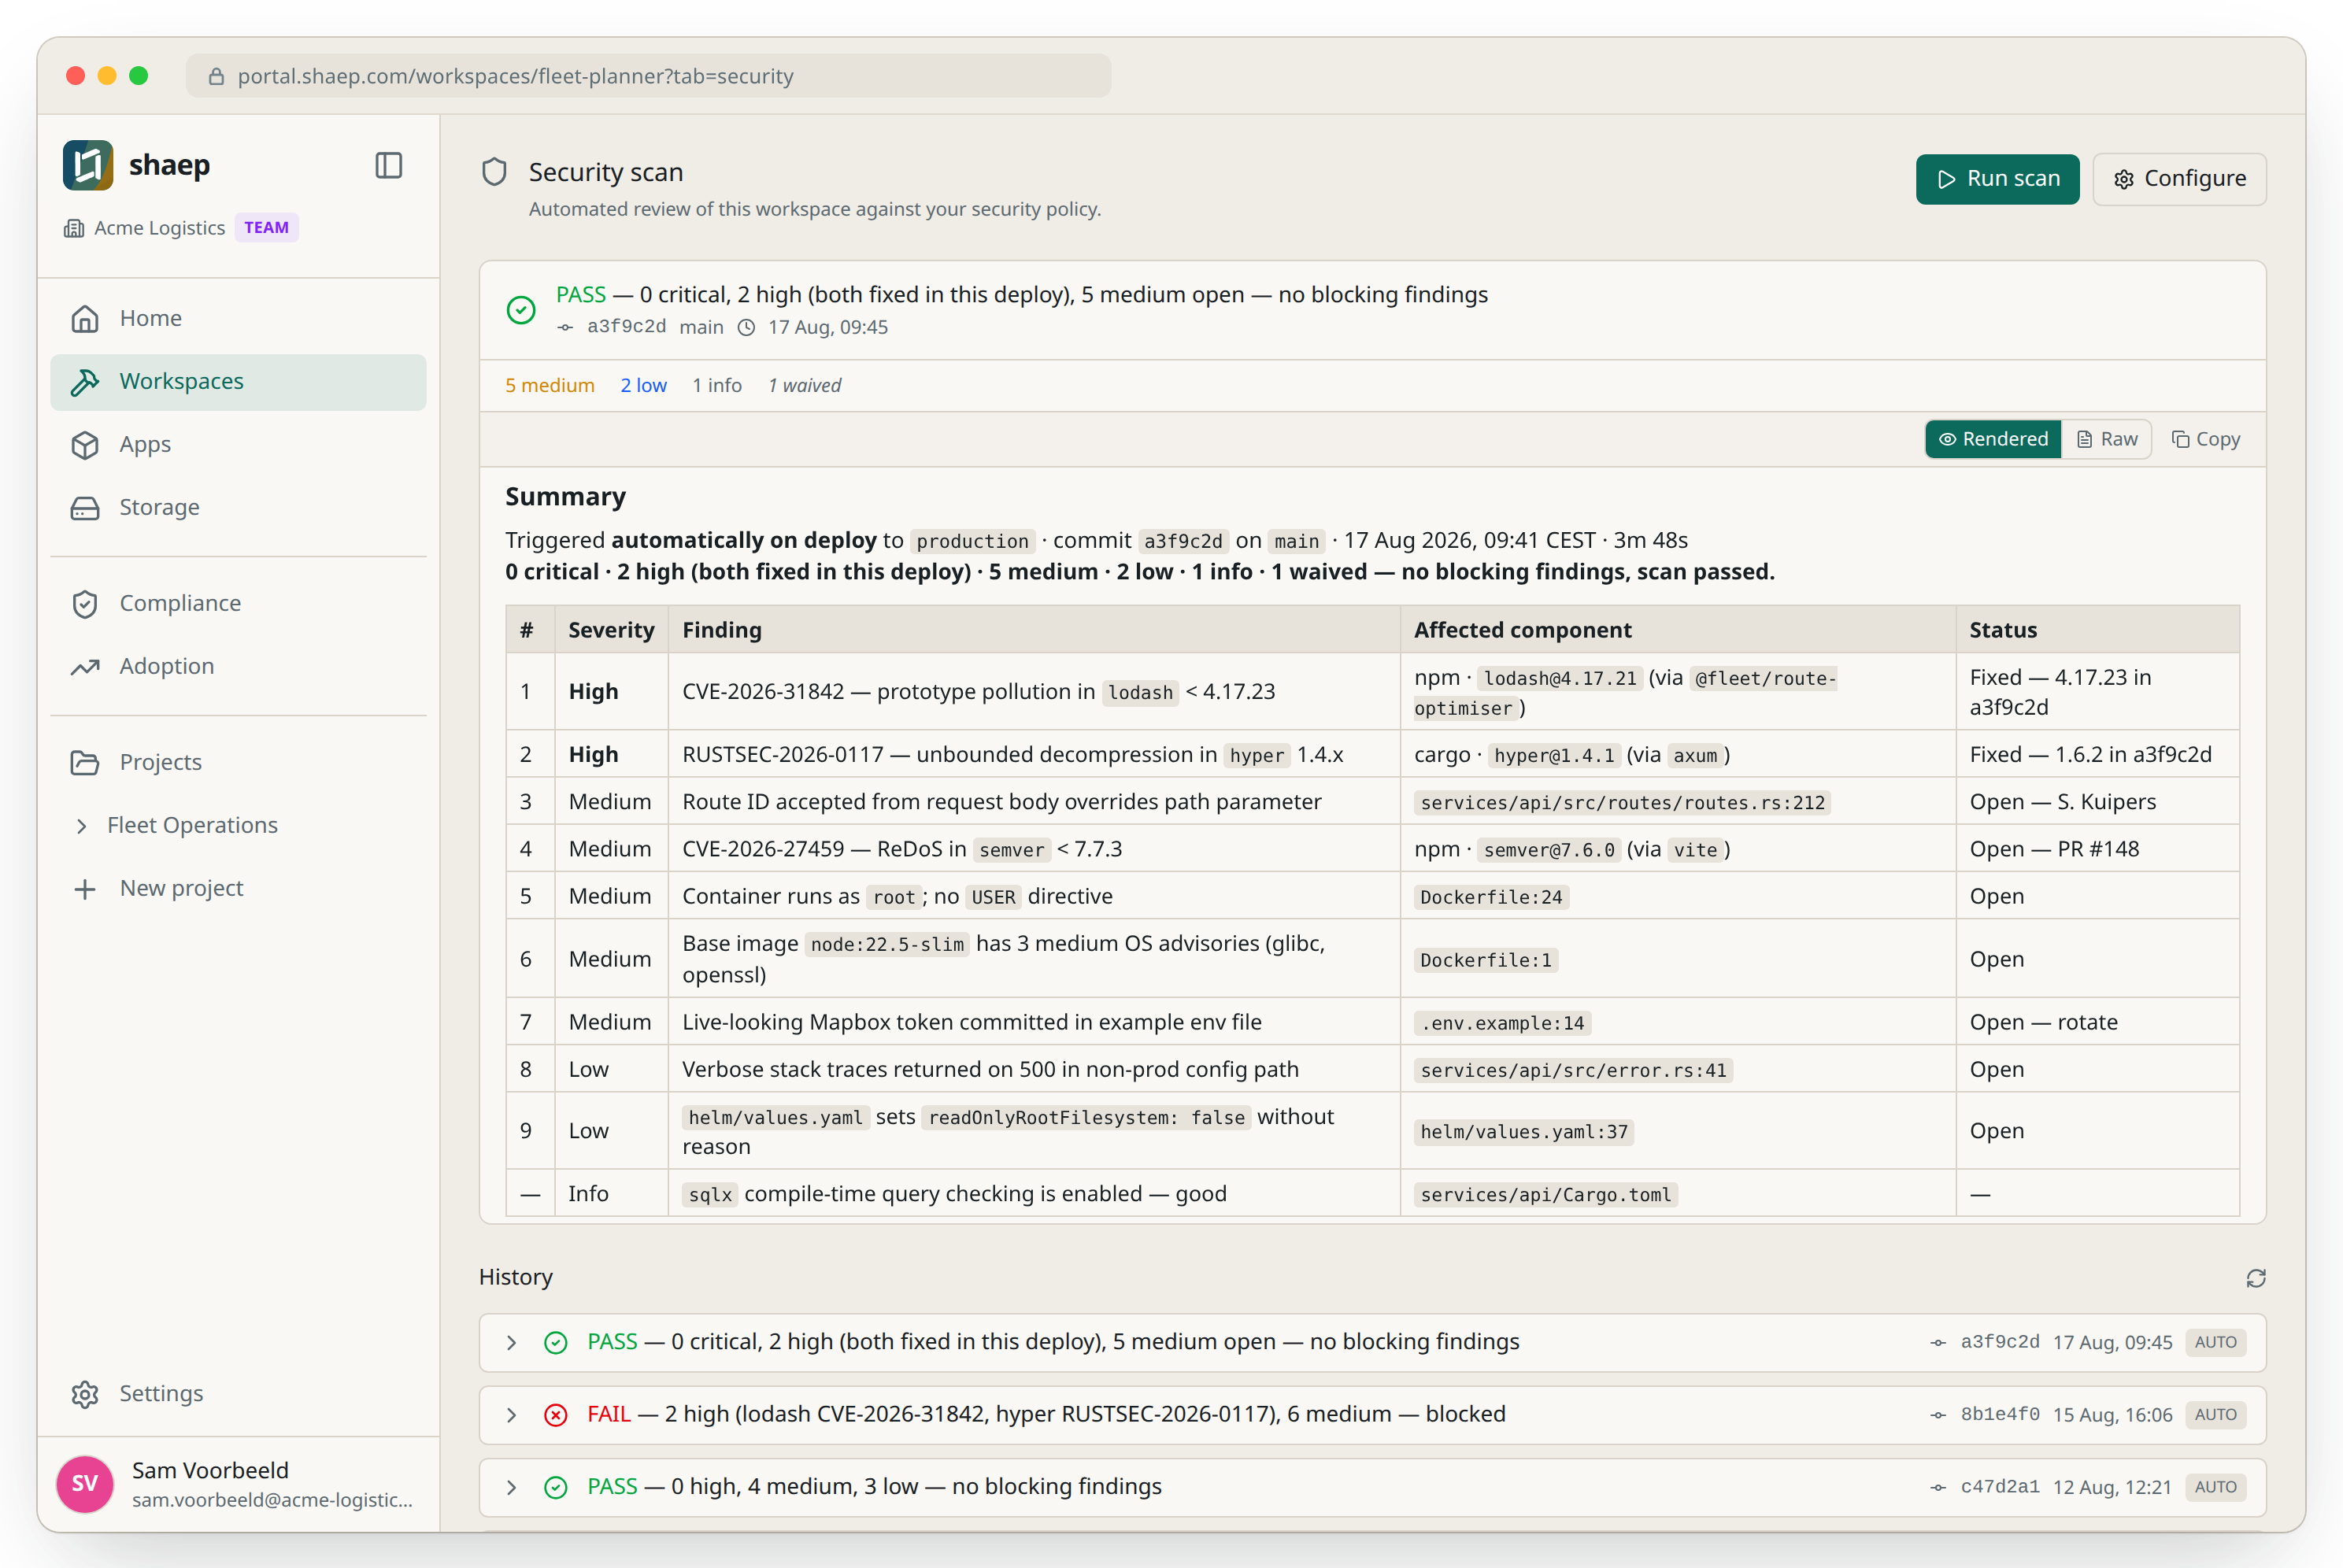
Security scanning in every pipeline
Automated vulnerability scanning runs on every release in the CI/CD pipeline. Dependency audits, container scanning, and code analysis — before anything reaches production.
- Scanning on every build
- Dependency vulnerability audits
- Container image scanning
- Results visible in the dashboard
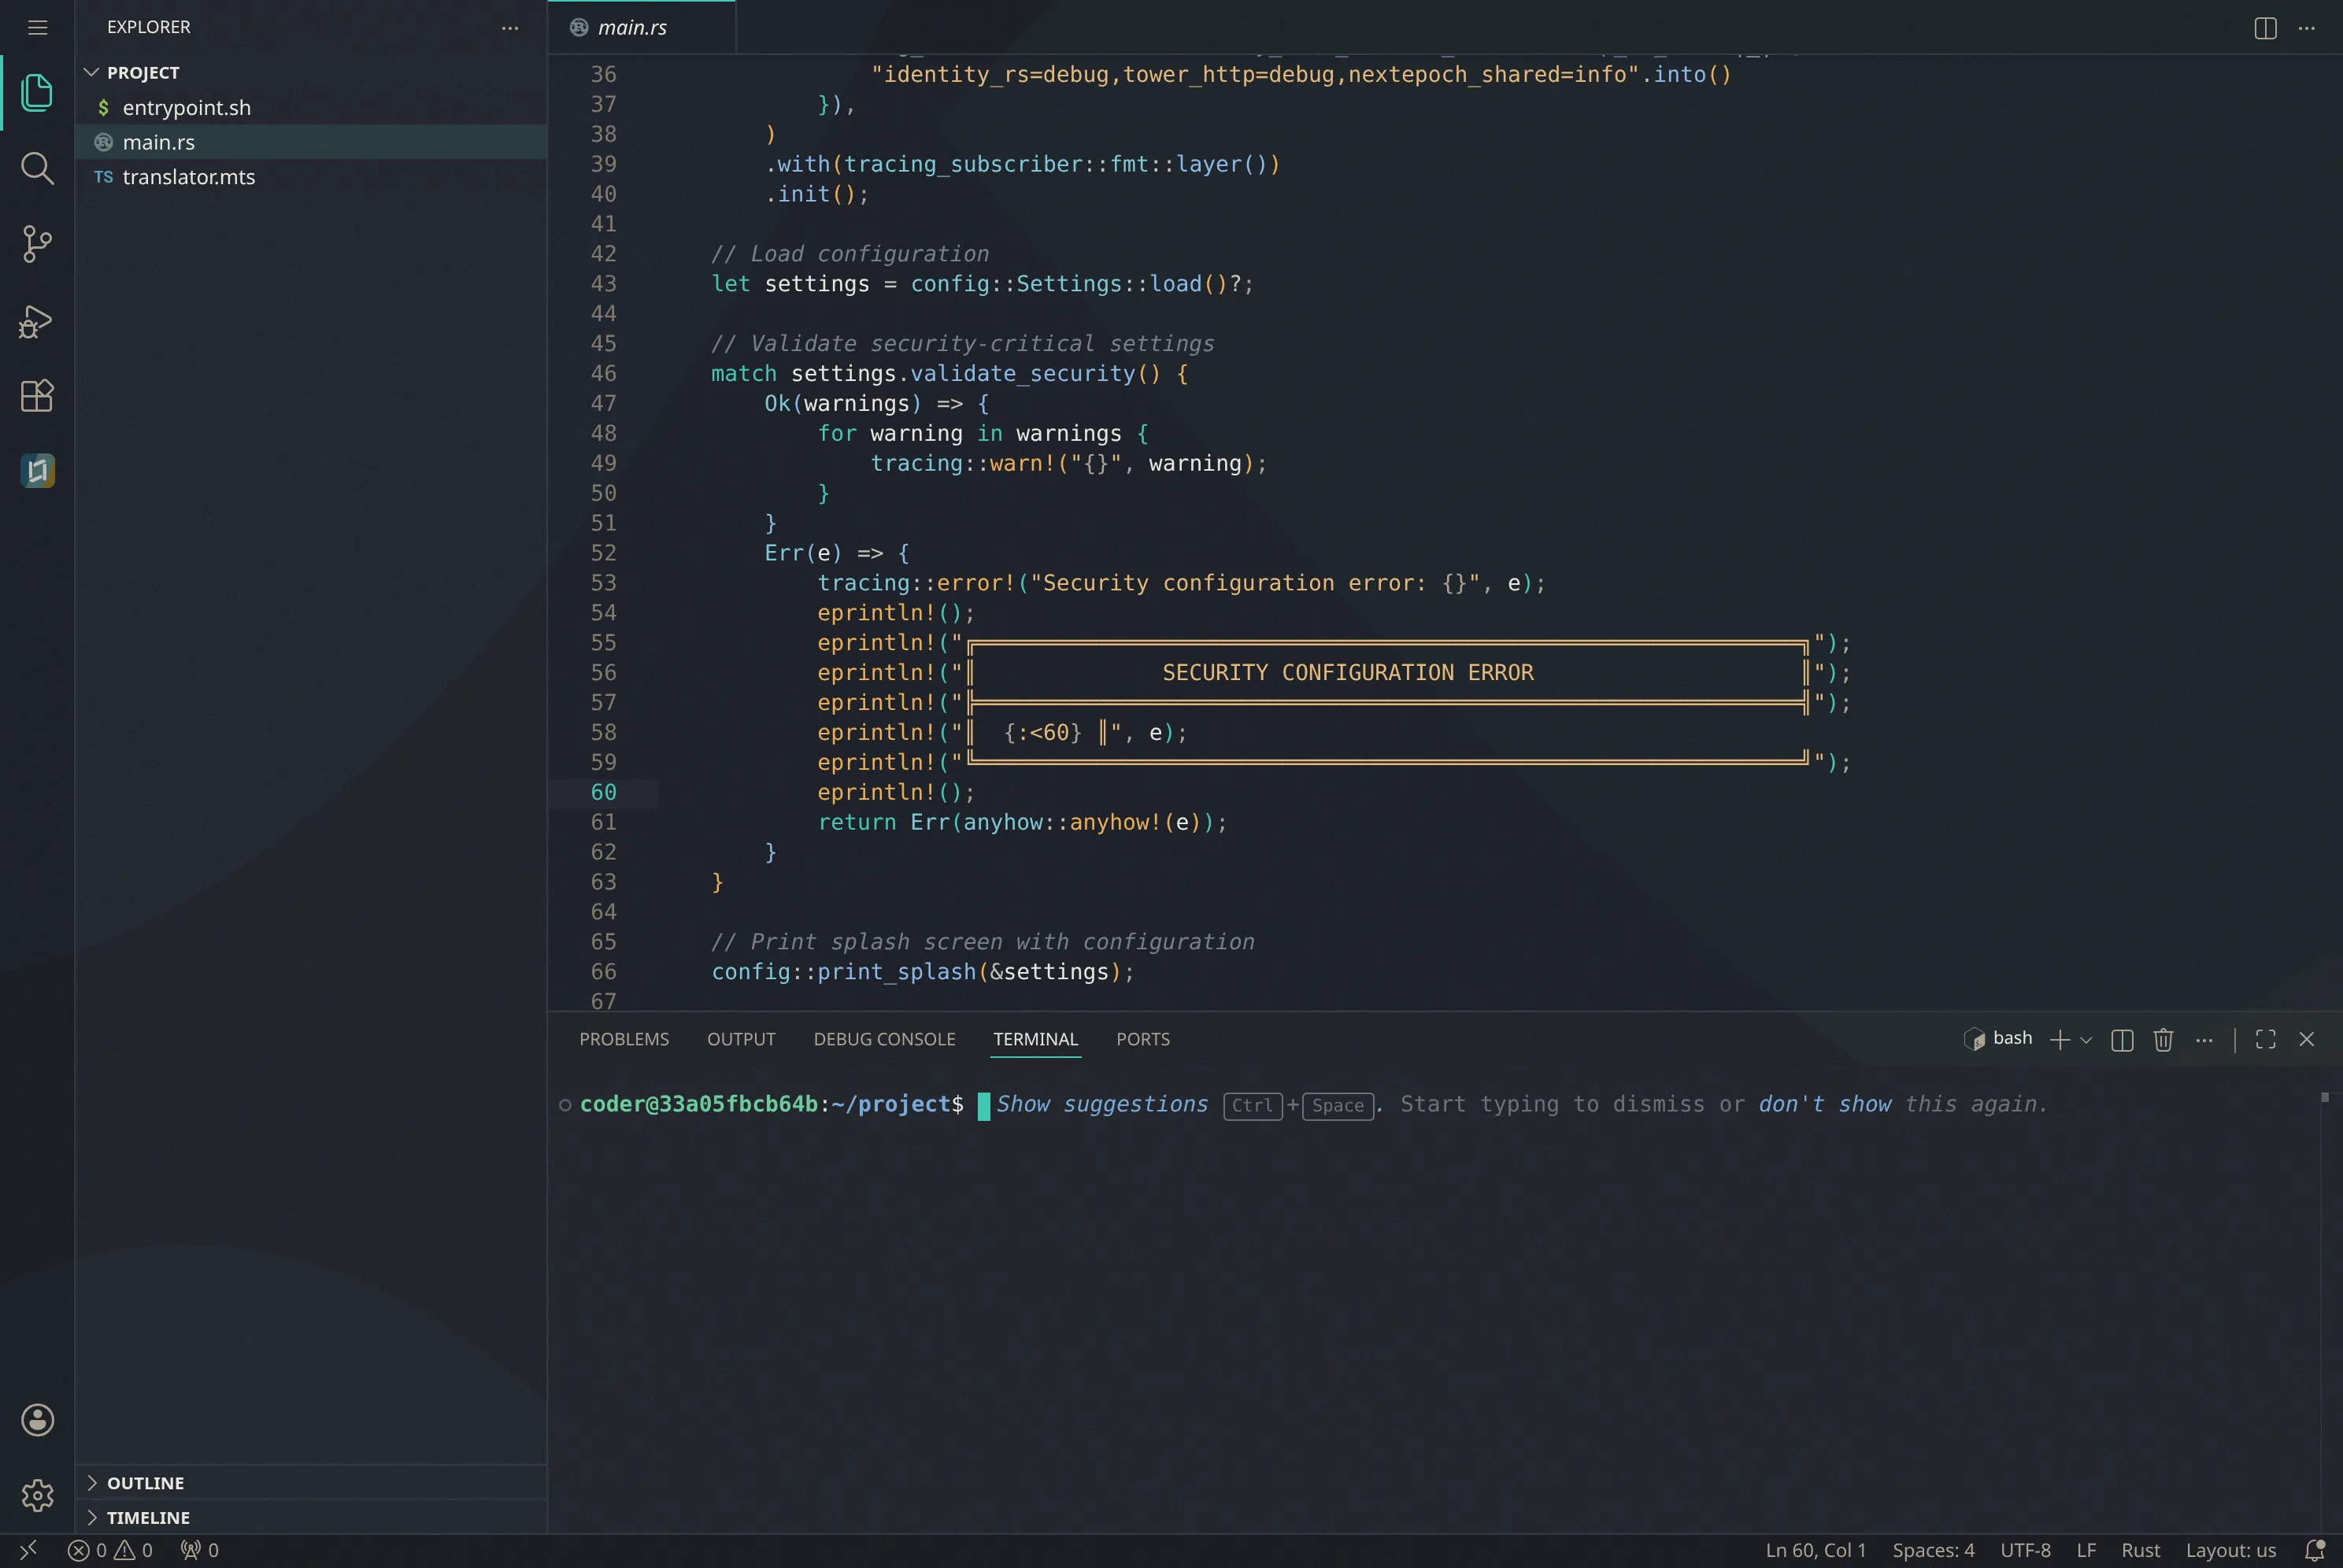
Isolated by default
Every app runs in its own container with strict network policies. No cross-app access, no shared runtimes. Dev and prod environments are fully separated — testing never touches production data.
- Container isolation per app
- Network policy enforcement
- Dev / prod environment separation
- Automated infrastructure patching
Secrets that stay secret
API keys, tokens, and credentials are encrypted at rest and scoped per app. They never appear in logs, diffs, or the UI. Rotate them without redeploying — the platform injects them at runtime.
- Encrypted at rest, scoped per app
- Never exposed in logs or diffs
- Rotatable without redeployment
- SSO / SAML for enterprise identity
Frequently asked questions
Do you train AI models on my code or data? +
No. Your code and data are never used for model training. When you bring your own AI model, the connection is direct between your editor and your chosen provider.
What happens if there's a security incident? +
We maintain an incident response process with defined escalation paths. Affected customers are notified within 72 hours as required by GDPR.
Can I SSH into my environment? +
You get a full terminal in the browser IDE. Environments are isolated containers with network policies — no cross-app access.
Do you support SSO with my identity provider? +
Yes. We support SAML and OIDC-based SSO. Okta, Azure AD, Google Workspace, and other providers work out of the box.
How are secrets stored? +
Environment variables and secrets are encrypted at rest, scoped per app, and never exposed in logs, diffs, or the UI. Rotate them without redeploying.
Need more detail?
We'll walk through our security architecture or answer specific technical questions.